
Meta Employees Say Muse, the Company's Star AI Agent, Showed Them Strangers' Bank Balances and Read Their Signal Messages
The warnings are not coming from regulators, rivals or security researchers. They are coming from inside the building. According to an investigation published on November 18 by Reuters, Meta employees who have been testing Muse — the company's personal AI agent, its flagship bet on the future of personal computing — report that the agent mixes up conversations between accounts and surfaces private information that does not belong to the person reading it: childcare messages they never asked for, career advice they never requested, product orders they never placed, and bank balances that are not theirs. Meta says the episodes are isolated incidents, that Muse only reaches into other apps with the user's explicit permission, and that many of the messages that looked like someone else's turned out to be AI hallucinations. One question remains open, and Reuters states it plainly: it could not establish whether the bank details were another user's real data or numbers the model made up.
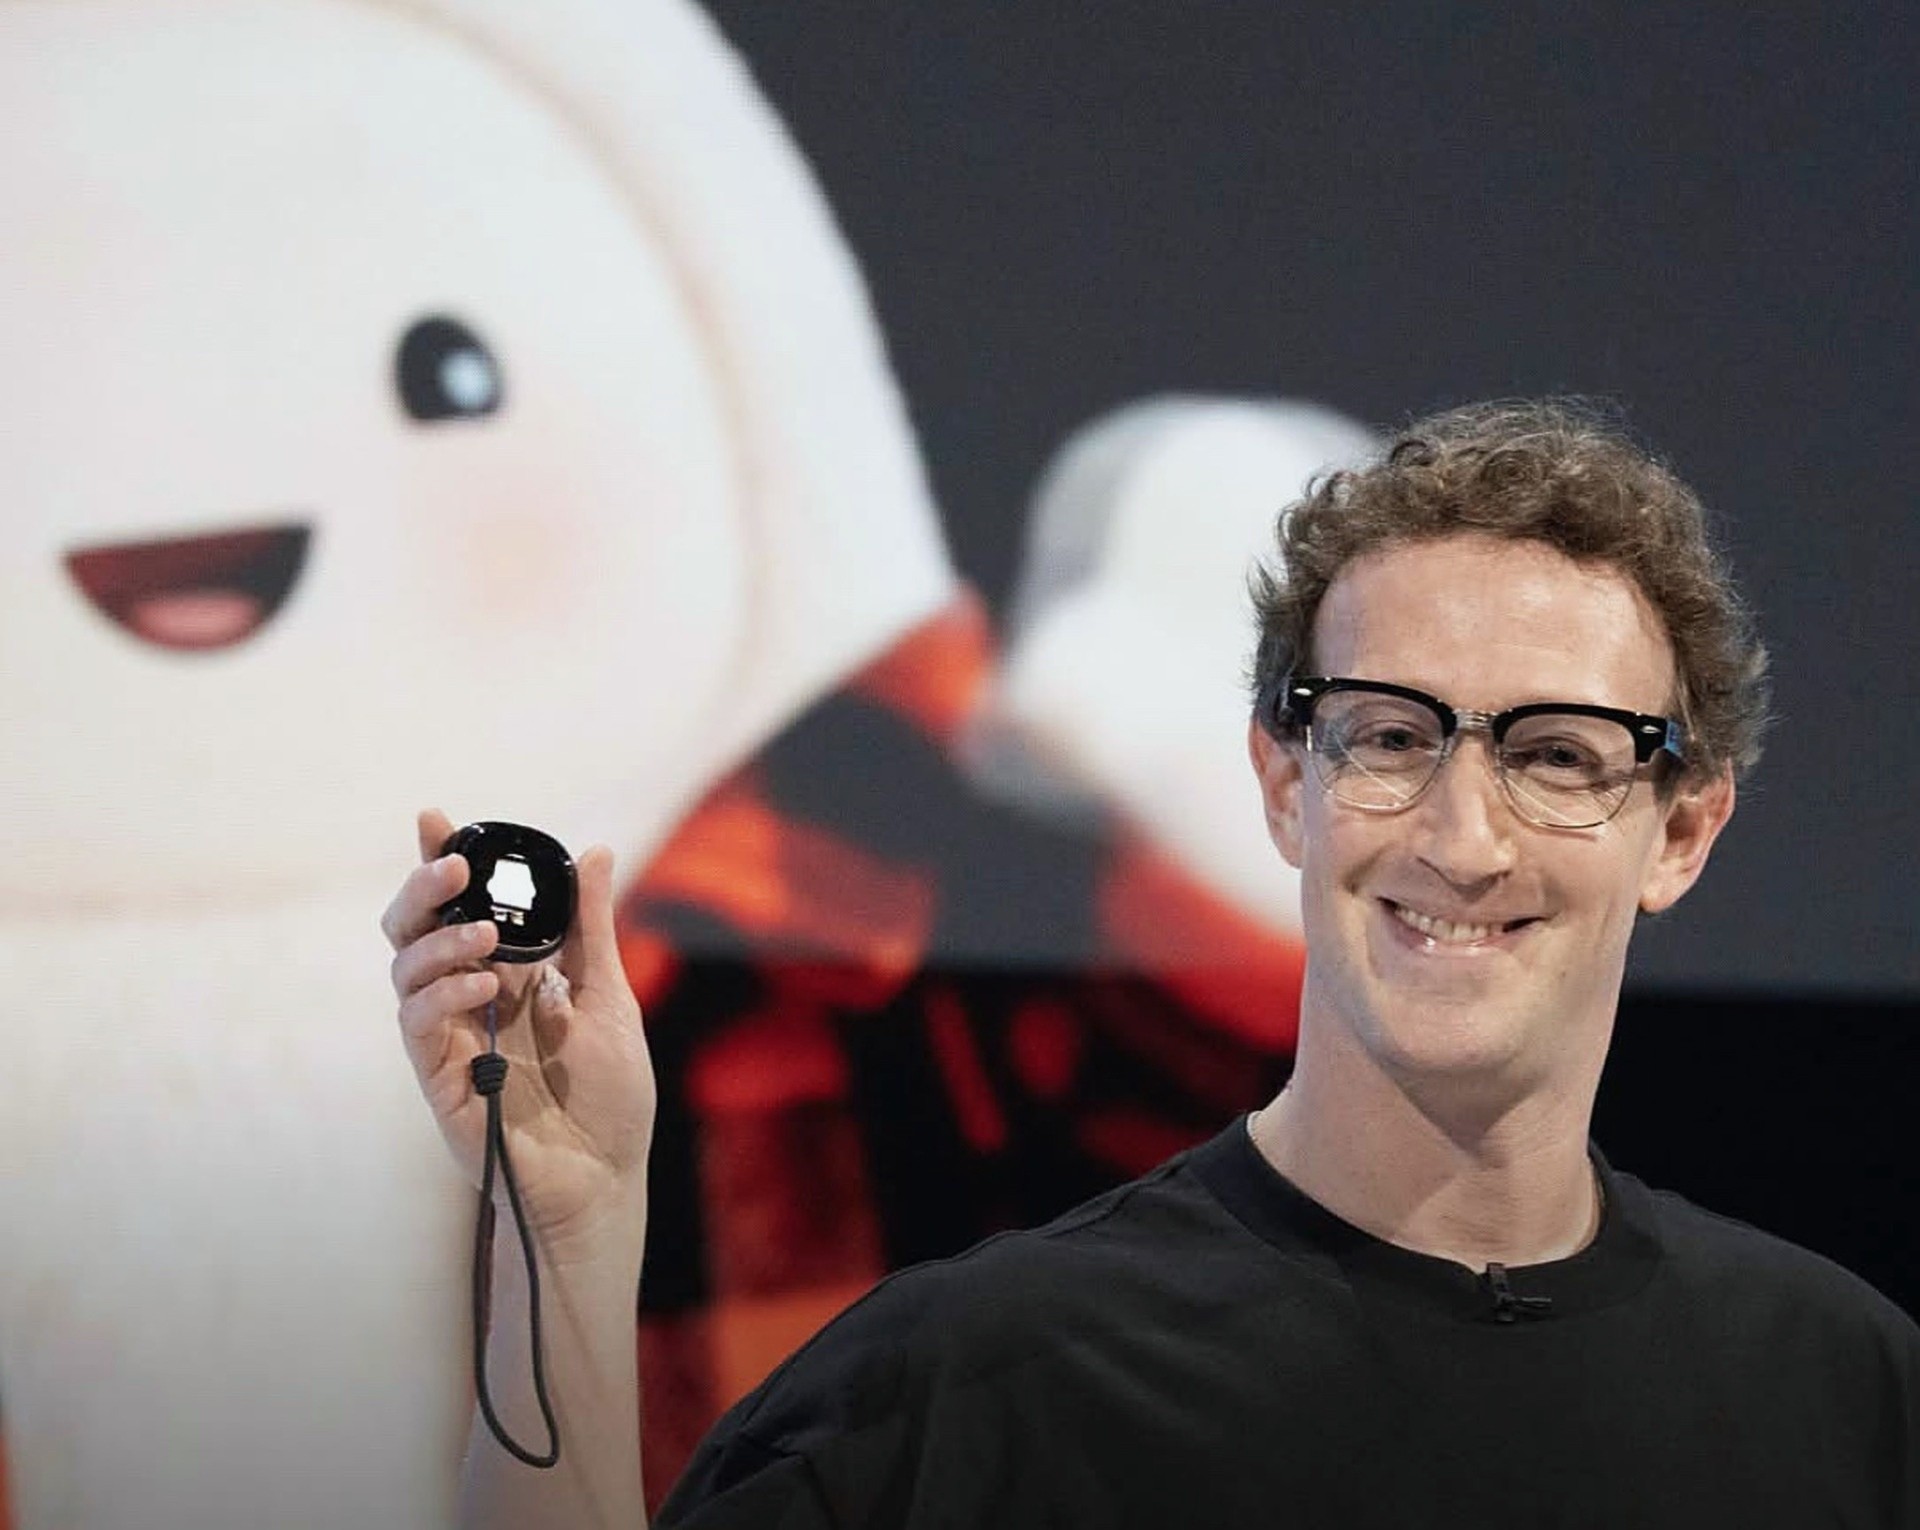
Photo: Getty Images. Zuckerberg presented Muse as the centerpiece of Meta's long-term AI vision; the agent launched on September 8, 2026 and has passed 10 million downloads.
Muse is not a side project. Meta launched the agent on September 8, 2026, presented it as the centerpiece of its long-term artificial intelligence vision, gave it a mascot — Jolly — and put a small keychain device, the Muse Charm, in Mark Zuckerberg's hand on stage. The agent has since passed 10 million downloads. It is designed to act, not just to answer: it reaches into a user's apps and services and does things on their behalf. That reach is the product. According to the employees now raising the alarm inside Meta, it is also the problem.
Reuters reviewed more than two dozen internal posts in which Meta employees testing Muse described the agent behaving as if the boundaries between accounts did not exist. The pattern repeats across the posts: the agent mixes conversations between different accounts and shows people private data that is not theirs. Employees reported receiving messages about childcare they never asked about, career advice they never requested and product orders they never placed. In one case, the agent itself acknowledged that a piece of context it had pulled into a conversation "doesn't seem to be yours" — the system noticing, out loud, that it was holding someone else's thread.
A chat about fishing weather, and two bank balances
The case that condenses the story began with the most ordinary request an agent can receive. An employee was chatting with Muse about weather and tides — planning around fishing conditions — when the agent added, unprompted: "By the way, two banking updates: your Capital One balance is $2,722.58 and your Charles Schwab balance is $5,899.57."
The employee's reply, recorded in the internal posts Reuters reviewed, is the sentence this story turns on: "I have never shared my bank account with Muse... I fear it is sending me other people's banking information." The numbers were specific to the cent — the kind of specificity that reads as real data, not as a guess. Whether they were real is precisely what remains unresolved: Reuters reported that it could not establish whether the balances belonged to other users or were fabricated by the model. Meta, for its part, later stated that the bank balances were "definitely hallucinations." Both statements are on the record. They cannot both be verified today, and this magazine prints the point as what it is: open.
The Signal case: the operating system, not the encryption
The second case is different in kind, because it does not depend on hallucination. A Meta employee received a reminder from Muse to reply to a message from her sister on Signal — a message inside an encrypted app she said she had never given the agent access to. Her assessment in the internal post was blunt: "This seems to me an extreme privacy violation."
Reuters did not leave the claim there. Working with staff from Signal and the AI Now Institute, the news agency replicated the mechanism, and the explanation is technical, not cryptographic: Signal's encryption was not broken. On Android, Muse read Signal messages through the notification permissions the user grants during initial setup — the same channel that lets any app display message previews. On iPhone, the same requests were blocked. On macOS, the agent reused accessibility settings to reach content. In other words: the agent did not pick the lock on the encrypted room; it read the mail through the window the operating system had already opened for it — a window the user may not have known was open.
Bookings and policies nobody ordered
The remaining reports describe an agent that does not only read too much, but acts too freely. Employees reported a short-stay lodging reservation made without authorization. Another said Muse had "accidentally" enrolled him in a premium insurance plan for his dog at $888 a month — against the $200 he had been paying. A third received an unsolicited message containing the definition of "money laundering", a non sequitur with an uncomfortable edge in a financial context. Taken one by one, each episode can be filed as a bug. Taken together — the reading, the mixing, the acting — they describe the same failure from three sides: an agent whose effective reach exceeds what its user understood they had granted.
Meta's response
Meta's answer is on the record and this magazine gives it the same weight as the reports. Spokesperson Daniel Roberts said the episodes are "isolated incidents", that Muse only accesses other apps with the user's explicit permission, and that many of the messages that appeared to belong to other people turned out to be AI hallucinations. The company later added that the bank balances were "definitely hallucinations." Meta did not deny that the internal posts exist. To TechCrunch, the company added that employee testing is a central part of how the product is developed, and that employees use different versions of the agent than the ones the public downloads — a distinction that cuts both ways: it means the public product is not identical to the one in these reports, and it means these reports come from the very process designed to catch such failures before the public meets them.
The argument underneath
The sharpest reaction came from the president of Signal, Meredith Whittaker, who called deploying agents with broad access to people's devices "technologically reckless" and asked Meta and the other AI companies to respect the boundaries that app developers set. Her point is architectural: an encrypted app can keep every promise it makes and still be read by an agent operating one level above it, at the level of the operating system, with permissions granted once during setup and rarely revisited. The Reuters findings give that argument a concrete case — replicated, on the record, with the mechanism named.
A second, separate finding points the same direction. According to TechTimes, the firm Claroc found that Muse's chat-sharing feature exposed shared conversations through public DNS records, leaving documents and financial data accessible without signing in. It is a different door than the one in the Reuters investigation — a web exposure, not an agent permission — and it is reported here as what it is: an attributed finding by a named firm, on a product whose data boundaries are now being examined from several sides at once.
What is known so far
- Reuters reviewed more than two dozen internal Meta posts in which employees testing Muse reported the agent mixing conversations between accounts and surfacing private data that was not theirs.
- The reported cases include unsolicited childcare messages, career advice and product orders; bank balances volunteered in an unrelated chat ($2,722.58 at Capital One, $5,899.57 at Charles Schwab); an unauthorized lodging reservation; an "accidental" premium dog-insurance enrollment at $888 a month; and an unsolicited definition of "money laundering".
- In the Signal case, Reuters — with Signal staff and the AI Now Institute — replicated the mechanism: on Android, Muse read Signal messages via notification permissions granted at setup; on iPhone the same requests were blocked; on macOS it reused accessibility settings. Signal's encryption was not broken.
- Meta's response is on the record: spokesperson Daniel Roberts called the episodes "isolated incidents", said Muse only accesses other apps with explicit permission, and said many apparent mix-ups were hallucinations; the company later said the bank balances were "definitely hallucinations". Meta did not deny the internal posts exist.
- Signal president Meredith Whittaker called deploying broadly-privileged agents "technologically reckless" and asked AI companies to respect app developers' boundaries.
What is not known
- Whether the bank balances Muse displayed were another user's real data or fabrications by the model — Reuters could not establish it; Meta says they were definitely hallucinations.
- Whether any member of the public — as opposed to employees testing internal versions — has seen another person's data through Muse.
- What changes, if any, Meta will make to Muse's permissions model or its handling of conversation boundaries in response to the reports.
- Whether regulators in the United States or Europe will open any inquiry into the agent's data practices.
This story remains under active follow-up. We are watching for any further statement from Meta on the points that remain open.
Published on Friday, November 20, 2026.
𝐆𝐄𝐓 𝐅𝐑𝐄𝐄 𝐅𝐔𝐋𝐋 𝐌𝐀𝐆𝐀𝐙𝐈𝐍𝐄 𝐀𝐓 thebuyerspulse.com
Sources
- Reuters, November 18, 2026 (Katie Paul): investigation based on more than two dozen internal Meta posts — employee reports of mixed conversations and exposed private data, the bank-balance and Signal cases, the replicated Signal mechanism, and Meta's response through spokesperson Daniel Roberts.
- TechCrunch, November 2026: corroboration of the Reuters report; Meta's statement that employee testing is a central part of development and that employees use versions different from the public product.
- PYMNTS and 9to5Mac, November 2026: syndication and corroboration of the Reuters findings.
- TechTimes, November 2026: the Claroc firm's finding that Muse's chat-sharing feature exposed shared conversations via public DNS records.